Enterprise defense. • Accessible to everyone. • Simple to deploy.

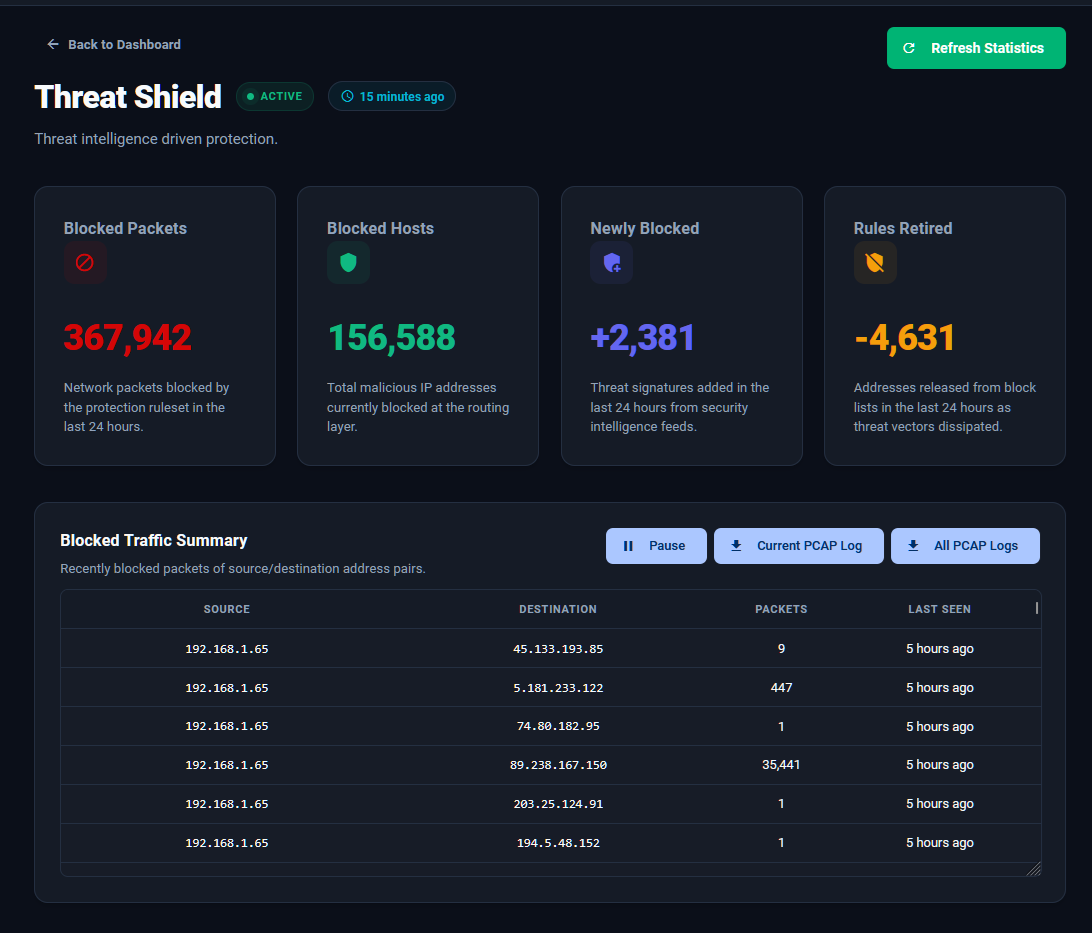
Threat Shield

Now Available
Traffic Protected: Calculating...

Smart protection.
Invisible presence.

Yazata is a physical shield that stops digital threats before they ever reach your devices. No software installations, no complex configurations. It simply does its job.

Set & Forget
Zero Configuration
L2
Transparent Bridge
< 1ms
Network Latency Added
100%
Automated Background Updates
System Traffic Telemetry
Approx. Real-time Metrics
Downloaded
--.-- Mbps
Uploaded
--.-- Mbps
Total Traffic Protected
--.-- Mbps

What does Yazata do?

Automated perimeter defense and egress filtering — zero endpoint footprint.

DNS-Level Threat Interception

Blocks requests to known phishing infrastructure and malicious domains at the network gateway, protecting endpoints before web content is retrieved.

C2 & Ransomware Kill-Chain Disruption

If an endpoint is compromised, Yazata severs external callbacks to command-and-control servers, halting secondary payload delivery and encryption key retrieval.

Dynamic Threat Intelligence Filtering

Aggregates real-time feeds to drop inbound automated scanning probes and hide vulnerable services from mass-scanning botnets.

Zero-Footprint Tracker Suppression

Silently drops telemetry connections and intrusive ad networks across all connected devices, reducing network latency and improving endpoint privacy.

Invisible Architecture.
Unchanged Network.

Most security appliances take total control: they dictate new rules to your router, change your IP addresses, and rewrite network routes. This approach frequently leads to configuration errors and frustrating downtime.

Yazata takes a completely different path. The device operates at Layer 2, acting as a so-called transparent bridge. This is the cleanest, most non-intrusive form of network architecture.

  • Zero network modification: Does not assign new IP addresses or alter your DHCP settings.
  • No routing interference: Does not redirect traffic down new paths or attempt to replace your existing router.
  • Untouched internal structure: Printers with static IPs, internal servers, NAS drives, and other hardware communicate exactly as they did before.

How does it work? (Interactive Network Flow)

Yazata sits seamlessly between your router and switch, filtering traffic in real-time.

Layer 2 Bridge Active
Internet
WAN Stream
Router
DHCP Gateway
YAZATA
Layer 2 Bridge
Switch
LAN Fabric
Wi-Fi AP Laptops & Phones
Wired LAN NAS, Servers & IoT
Yazata Shield:
Status: Shield is active. Safe data flowing through Switch & Wi-Fi AP.

The Power of Prevention.

Traditional security systems wait for trouble to strike. They wait until the threat knocks on your network's door, and only then do they try to stop it. Yazata works differently. Driven by Threat Intelligence, the device already recognizes the attacker before they even head toward your network. This isn't damage control — it is pure prevention.

Collective Memory

If a new digital threat emerges anywhere in the world—whether on a remote server or a network on another continent—the global network instantly identifies and analyzes it.

Immediate Immune Response

The moment a risk is recognized, Yazata updates its internal database within seconds. Your network automatically receives immunity before the wave can even reach you.

Digital Fingerprints

The system monitors the behavior and digital signatures of suspicious sources. As a result, known fraudulent websites and malicious command-and-control servers are caught in the filter instantly.

YAZATA Threat Intelligence Data Flow

Monitor how real-time security rules flow from threat research centers to your protected Yazata devices.
Yazata Threat Intelligence data flow visualization
// YAZATA THREAT INTELLIGENCE DATA FLOW — SYSTEM OPERATION DURING A LIVE ATTACK

[ STAGE 1 · GLOBAL THREAT RESEARCH — CONTINUOUS, 24/7 ] ──► Distributed Honeypots · AI Behaviour Classifier · Partner CERT Feeds
  → Extracts attacker IP addresses, C2 domains and malicious signatures into raw indicators.
                       │ (automated polling & synchronization)
                       ▼
[ STAGE 2 · YAZATA CENTRAL NORMALIZATION ENGINE ] ──► Parsing · Deduplication · Whitelist sanitization
  → Collapses the raw indicators into ONE compact, digitally signed rule set: the live threat database.
                       │ (rule push: several times per minute — instantaneous during a surge)
                       ▼
+----------------------------------------------+
| YAZATA SHIELD (Physical Layer 2 Inline Unit) | ►── rules enforced at kernel level, before any host is reached
+----------------------------------------------+
                       │ (transparent transit — zero reconfiguration, no software agent)
                       ▼
[ STAGE 3 · LIVE ATTACK INTERCEPTION ]
  → Inbound port scan / phishing callback / botnet C2 beacon → DROPPED at Layer 2 (source-IP rejection).
  → Clean business traffic passes through untouched, at line rate.
                       ▼
[ PROTECTED LOCAL NETWORK ] Workstations · Servers · IoT · Wi-Fi Access Points

Why is this a complete game changer?

Most modern cybersecurity incidents are automated. Millions of botnets continuously scan the online landscape, tirelessly searching for open ports. Equipped with Threat Intelligence, Yazata filters out this massive background of digital noise and aggression every single second. You don’t need to read the news, and you don’t have to hassle with manual updates.

Security that helps. Not hinders.

We believe that adding a new device to a network should bring peace of mind, not anxiety about Monday morning downtime.

Respecting the Sysadmin’s Work

We believe that one of Yazata’s greatest values is what it doesn't do. It never interferes with the infrastructure your IT professionals have carefully built.

  • Zero conflict: Does not overwrite existing firewall rules, does not clash with internal systems, and creates no redundant loops.
  • No added workload: Won’t generate a constant stream of false positives or alert fatigue that waste IT staff's valuable time.
  • An invisible teammate: Handles the heavy lifting of network hygiene in the background, without taking any control out of local hands.

Uninterrupted Daily Routines

The best security system is the one your employees don't even know is there. Yazata does not force its presence on people who simply want to get work done.

  • No disruptive pop-ups: It never disrupts workflows with unexpected alerts, blocking screens, or browser permission prompts.
  • Zero latency / slowdowns: Highly optimized internal switching fabric ensures network speeds and ping rates remain unaffected.
  • It simply works: Your team browses the web, handles secure emails, and uses corporate tools exactly as they always have.

Technology that adapts.

Yazata was created to eliminate the complexity of enterprise defense. Seamlessly blending into any setup.

It simplifies their work.

Yazata is not here to replace your existing IT infrastructure or firewall configurations, but to support and augment it.

Respects your architecture

Thanks to its transparent Layer 2 operation, it does not interfere with your established routing rules, NAT setups, or internal VLAN structures. It causes zero configuration conflicts.

Lightens the daily workload

It takes the daily chore of filtering global threats and digital noise off your administrator's shoulders, without generating additional syslog noise, complex dashboard alerts, or support tickets.
It simply works.

Security shouldn't require an engineering degree. We designed Yazata so that anyone can start using it immediately, even without a technical background.

Zero configuration

There are no complex settings to learn, no dashboards to configure, and no confusing technical jargon. It manages itself completely.

Plug and play

Installation is as simple as plugging in the cables. From that exact moment, the system protects every device on your network automatically and autonomously in the background.

1
Connect router LAN port to WAN IN.
↓
2
Connect switch port to LAN OUT.
↓
3
Fully secured. No setup required.

Deep DNS Filtering

The internet is full of noise—intrusive ads, heavy trackers, and hidden scripts that slow down your business and compromise your privacy. Yazata changes that at the foundational level.

Network-Wide DNS-Layer Security

Enterprise networks are overwhelmed by noise: invasive ad servers, background telemetries, and tracking scripts that consume bandwidth and expose internal endpoints. Yazata addresses this at the name-resolution layer.

Autonomous Traffic Hygiene

Powered by an inline, high-throughput DNS filtering engine, Yazata intercepts and evaluates outbound lookups before socket connections are formed. It enforces corporate traffic hygiene in real time without client-side agents.

  • Zero-Configuration Ad Suppression: Eliminates the need for client browser extensions or per-device policies. Yazata sinkholes ad networks and intrusive banners across every device on the segment — including IoT, mobile, and guest endpoints.
  • Telemetry & Tracker Mitigation: Third-party analytics and tracking networks continuously profile internal activity. Yazata silently drops these query resolutions, preserving network privacy and reducing outbound footprint.
  • Malicious Domain Interception: When an internal endpoint attempts to resolve known phishing infrastructure, botnet nodes, or malware distribution domains, Yazata denies resolution instantly (returning NXDOMAIN / Sinkhole IP), containing the risk at the physical boundary.
"We believe security shouldn't feel heavy. By filtering the noise at the DNS level, your network doesn't just become safer—it becomes noticeably faster, cleaner, and lighter."

Key Benefits for Your Business

Zero Footprint

It works completely in the background without affecting browser performance or device battery life.

Vendor Independent Defense

Because the filtering happens at Layer 2, browser updates or platform restrictions cannot bypass or disable your protection.

Bandwidth Optimization

By stopping heavy ad networks and telemetry scripts from loading, your actual network bandwidth is saved for what truly matters: your business operations.

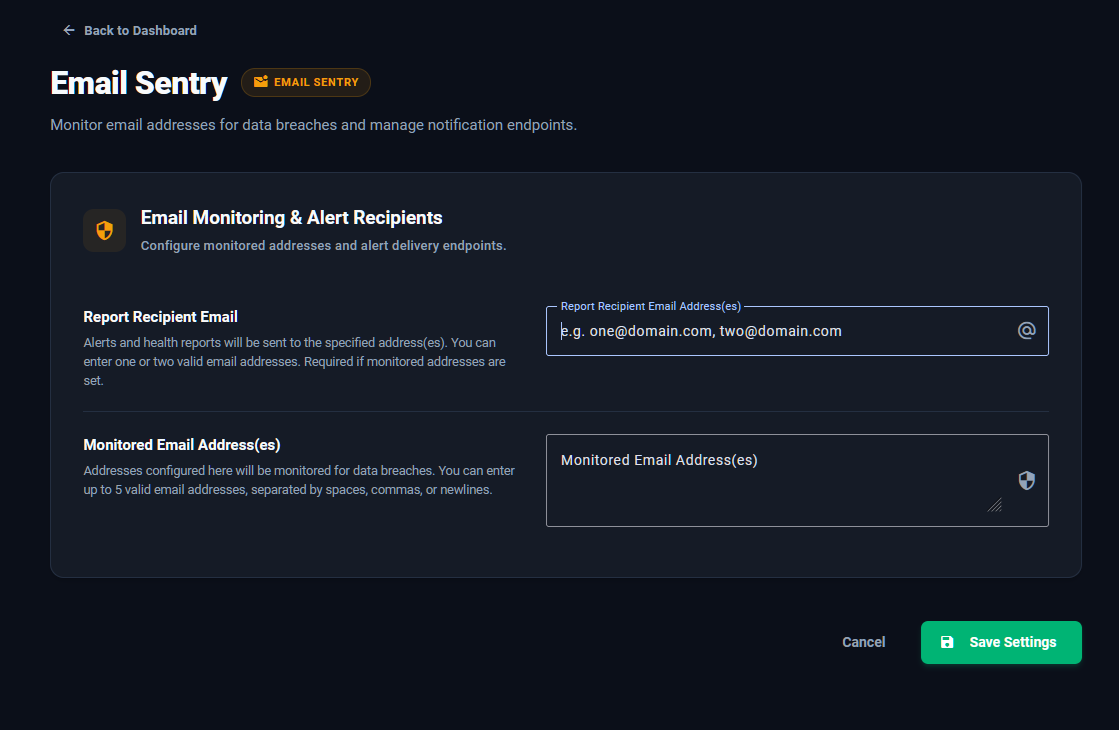
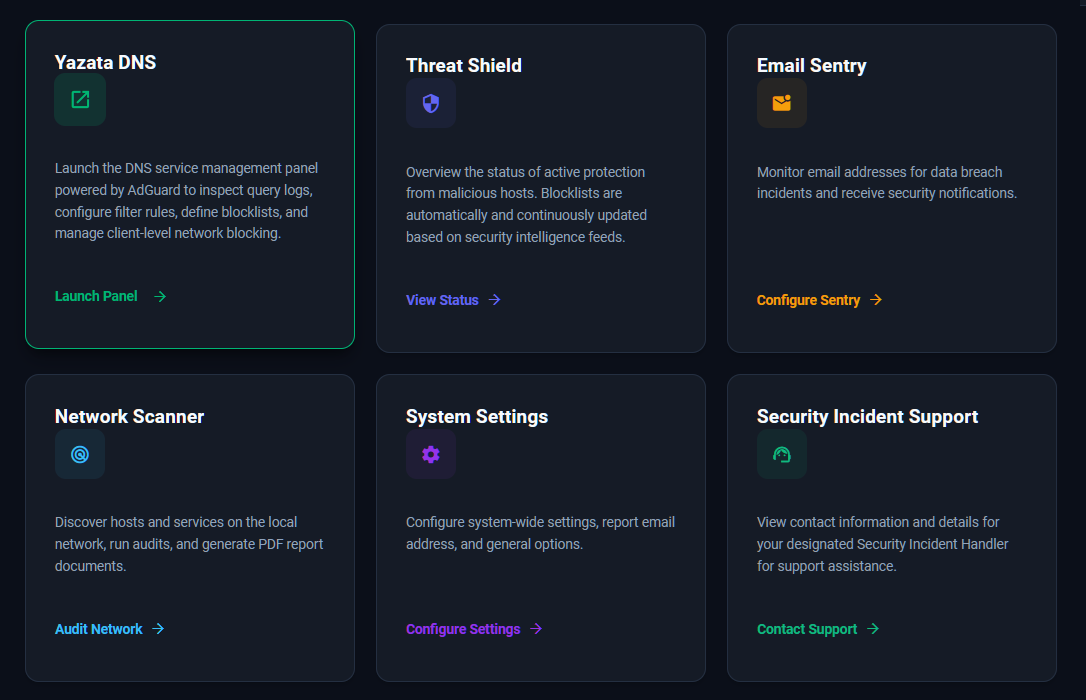
Email Sentry

Continuous, 24/7 digital surveillance monitoring your email addresses against global data breaches and dark web sources.

Security Incident Support

Immediate response defense tier providing direct access to specialized operations managed by our qualified partner, Trust Shield Global Zrt.
Security Incident Support — Response Operations

When Seconds Matter, We Respond.

Immediate response defense tier providing direct access to specialized operations managed by our qualified partner, Trust Shield Global Zrt.

  • Automated Escalation & Rapid Engagement: Defense unit initiates immediate containment and mitigation protocols.
  • Dual-Track Remediation (Technical & Legal): Technical countermeasures (forensics, containment, system restoration) combined with legal/regulatory support (GDPR/NIS2 breach reporting).

Accreditations and Security Clearances

  • Constitution Protection Office (AH) accreditation
  • ISO/IEC 27001 Information Security Management Certification
  • EU, NATO, and National 'Confidential' level security clearances (ETBT registries)
  • All partners and principals hold official national security vetting.

Deploy Inline Perimeter Defense
Without Re-architecting Your Network

Integrate the Yazata security appliance seamlessly into your existing infrastructure as a transparent Layer 2 bridge. Eliminate blind spots and suppress outbound threat vectors immediately — with zero disruption to your daily operations.

  • Zero Topology Changes: Drops directly between your modem/router and core switch without subnet re-addressing, NAT modifications, or firewall rule rewrites.
  • 100% Agentless Architecture: Automatically protects every connected endpoint, including unmanaged IoT devices, smart TVs, and legacy hardware that cannot run EDR agents.
  • Immediate Threat Suppression: Synchronizes with global threat intelligence feeds upon power-up to silently drop malicious traffic and sever C2 callbacks.